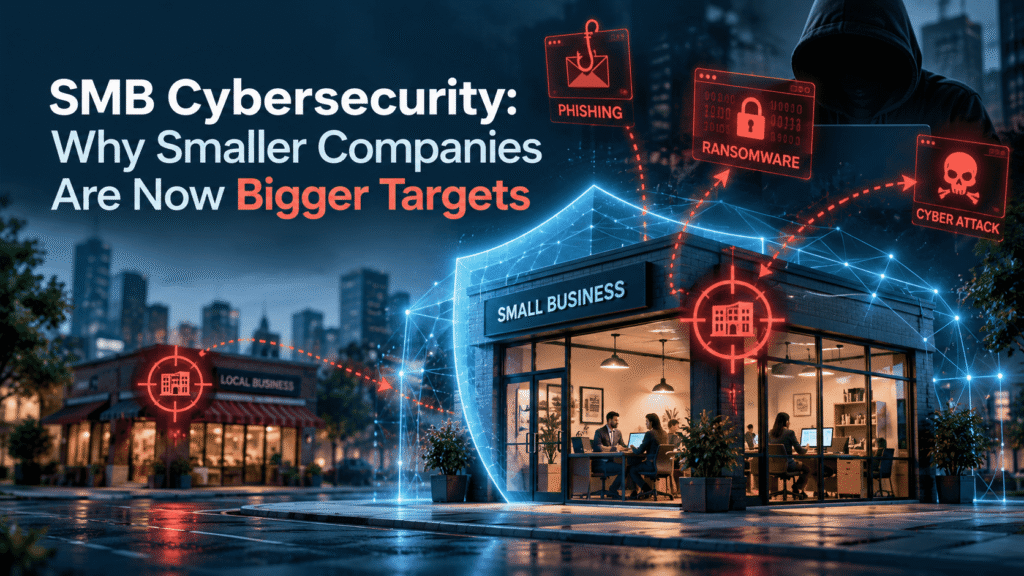
SMB Cybersecurity: Why Smaller Companies Are Now Bigger Targets
Cybercriminals used to follow a simple playbook. Target large enterprises with deep pockets and established security budgets. Smaller companies got overlooked, treated as too much effort for too little payoff.
That era is over.
Small and mid-size businesses (SMBs) have become the preferred target for attackers across the threat spectrum. Ransomware groups, credential stuffers, and opportunistic threat actors actively hunt SMBs because the math works in their favor. You have enough value to extort but not enough defenses to stop them.
This shift in targeting strategy changes everything about how SMB security teams approach their work. It’s no longer enough to “do what you can with limited resources.” You’re now operating in an environment where attackers have specifically engineered tactics to exploit the gaps between enterprise-grade security and no security at all.
The Economics of SMB Targeting
Let’s start with why this happened. Ransomware economics make SMBs exceptionally attractive.
An enterprise with 5,000 employees and 500 security staff represents a hard target. Multiple detection layers, incident response teams, air-gapped backups, and the institutional knowledge to survive an attack without paying. A successful breach requires weeks of careful reconnaissance and custom tooling. Many attacks fail before they reach their goal.
An SMB with 50 employees and one overworked IT person is a different proposition. A script will find the exposed RDP port. Credentials from a password breach will work. Once inside, backups are often connected to the same network. The owner, seeing operations completely halted, has a choice: rebuild from scratch over weeks, or pay a ransom that seems reasonable when the business is hemorrhaging money per day.
This is the core calculation attackers make. Not “will we succeed.” But “how many SMBs can we successfully compromise before defenses catch up?”
The market adapts accordingly. Ransomware-as-a-service operations now publish price lists with SMB-specific offerings. Attack toolkits are engineered for speed and stealth in small environments where monitoring is sparse. The barrier to entry for conducting attacks has never been lower.
Common Vulnerabilities in Smaller Organizations
SMBs share a vulnerability profile that differs from enterprises not just in degree but in kind.
Resource constraints are real. An enterprise can afford a full security stack: endpoint detection and response, identity and access management, security information and event management, threat intelligence. An SMB picks two or three of these, maybe. Often, the choice is made based on what the managed service provider recommends, not what the business actually needs.
Complexity creates blind spots. You don’t know what you don’t see. An SMB often has systems that nobody fully understands. A legacy accounting application that runs on someone’s workstation. A file server that’s been running since 2015 with the same local admin password. A cloud storage account that everyone shares credentials for. These systems persist because they work and replacing them costs money and time.
Patching discipline falls apart. Large organizations enforce patching schedules. Small ones don’t. A critical vulnerability drops on Tuesday. The SMB IT person is busy with password resets and printer issues. Two months later, the vulnerability is still unpatched. An attacker scanning for that specific vulnerability finds the SMB and moves in.
Credential hygiene is poor. Passwords are reused across systems. Default credentials never change. Service accounts use the same password everywhere. This means one compromise often means multiple systems are compromised. An attacker finds the network admin’s email password in a breach database and can now reset every system on the network.
Third-party risk goes unmanaged. SMBs rely on vendors, consultants, and integrations. Cloud accounting software with API access to the bank. A backup vendor with full system access. An e-signature vendor that integrates with email. Each one is a potential pivot point for attackers. Most SMBs have no visibility into what these third parties can access.
User awareness is minimal to nonexistent. Employees receive no security training. Phishing emails get opened because there’s no reason not to. USB drives found in parking lots get plugged in. A customer email address gets added to the wrong group because nobody checked. Social engineering works reliably because the organization hasn’t developed any resistance to it.
A Realistic Example: Manufacturing Supply Chain Attack
Consider this real scenario: a small manufacturing company with 35 employees, annual revenue around 4 million dollars.
They use QuickBooks for accounting, a customer portal built on WordPress, and email hosted through a common provider. Their operations are largely on-site: machines, local computers, and a NAS appliance for file storage.
An attacker finds the WordPress admin password in a breach database from a totally unrelated website. The password works because the owner used the same password everywhere. The attacker gains access and adds a backdoor plugin.
The backdoor silently harvests login credentials from customers visiting the portal. Among those credentials are admin accounts for customers’ own systems. The attacker sells these credentials on a dark web forum.
A few weeks later, the manufacturing company receives a ransom demand. The attacker has compromised several of their largest customers using credentials harvested from the stolen portal. The attacker threatens to shut down the customers’ operations if the manufacturer doesn’t pay. The customers are furious. The manufacturer is liable in their eyes.
The entire incident was preventable with five minutes of work: a password manager, a strong unique password, and WordPress security updates. None of these things happened because the owner was focused on customer service and revenue, not cybersecurity.
This is how SMBs actually get compromised. Not through advanced persistent threats or zero-day exploits, but through the same low-effort tactics that work every time because the defenses aren’t there.
The Ransomware Epidemic
Ransomware has become the primary business model for cybercrime affecting SMBs.
Unlike previous generations of malware that destroyed data for fun or stole credentials for espionage, ransomware creates a direct financial incentive to pay. Your data is encrypted. Your business stops. You can either rebuild over weeks or pay thousands of dollars to get your keys back.
SMBs face a brutal choice that enterprises often don’t. An enterprise can invoke business continuity plans, recover from backups, and sustain the impact for days or weeks. An SMB cannot. A three-day outage at a small company can be an existential threat.
Ransomware groups know this. They specifically adjust their ransom demands based on company size. They study the target’s insurance, customer base, and revenue before making their ask. They know what amount the owner is most likely to pay without declaring bankruptcy.
The professionalization of ransomware operations has made this threat unavoidable for SMBs. It’s not a question of if you’ll face ransomware but when. Your preparedness determines whether you pay, recover, or close.
Why SMBs Delay Security Investment
Understanding the targeting of SMBs requires understanding why security improvements don’t happen faster.
Opportunity cost is immediate. Money spent on security is money not spent on product development, marketing, or hiring. The owner sees the choice as binary: hire a salesperson or hire a security consultant. They choose the salesperson because sales revenue is tangible and immediate.
Risk feels abstract. The company hasn’t been breached yet. The owner hasn’t experienced the impact. Statistics about SMB compromise rates feel like background noise. This changes instantly after a breach, but by then, it’s too late.
Security vendors are expensive and complex. The average SMB has looked at enterprise security tools, found them unaffordable, and given up. Few vendors market to the SMB space effectively. The ones that do often lack the depth of larger vendors. Budget and complexity create paralysis.
Competent security staff is scarce. Finding someone who can assess your security posture, recommend improvements, and help implement them is harder than finding developers or marketers. The SMB IT person is usually a generalist who maintains systems but doesn’t have security expertise. They’re unlikely to advocate for investments they don’t fully understand.
Practical Security Measures for SMBs
Despite these challenges, SMBs can achieve a meaningful security posture without enterprise budgets or headcount.
Prioritize asset inventory. You can’t protect what you don’t know you have. Spend a day mapping your systems: computers, servers, storage, applications, cloud services, and vendor integrations. Document who has access to each. This exercise alone often reveals surprises that are easy to fix.
Enable multi-factor authentication everywhere. Email, cloud storage, remote access, financial systems. If a password is compromised, MFA stops most attacks at the gate. This is the highest-ROI security control available to SMBs. Implement it first.
Patch consistently. Not perfectly. Consistently. Establish a routine: patch on the first Tuesday of each month, or align with vendor schedules. Don’t let patches sit for months. This eliminates the majority of exploitation opportunities.
Use password managers. Every user gets one. All passwords are unique. Shared credentials become a relic of the past. This is the fastest way to eliminate compromised credentials as a attack vector.
Segment your network. Keep customer data separate from operations. Financial systems separate from general office systems. This limits the blast radius if one system is compromised. Even a simple firewall rule separating systems is valuable.
Back up everything offline. Not just to a connected NAS. At least one backup must be disconnected from your network. If ransomware hits, you need a clean copy you can restore from without paying.
Control administrative access. Most users should have standard user accounts. Only administrators use admin accounts. Log out of admin accounts when not in use. This prevents malware from running with admin privileges.
Document your incident response plan. If you’re breached, you’ll be in crisis mode. You need a written plan that says who calls who, what information you preserve, and what your recovery steps are. You’ll never follow it perfectly, but having it reduces response time significantly.
Start here. These eight items cover the majority of attacks against SMBs. They don’t require vendors, consultants, or expertise beyond discipline and follow-through.
The Hidden Cost of Poor Awareness
Technical controls matter. But the reality is that most successful breaches start with a human mistake.
An employee opens a phishing email and clicks a malicious link. A contractor shares login credentials over email. An executive receives a spoofed email that looks like it’s from the bank and transfers money to the wrong account. A user plugs an unknown USB drive into their workstation. These incidents happen constantly.
Employee awareness training is often treated as compliance theater: a required annual webinar that nobody pays attention to. This approach fails because it doesn’t change behavior. Effective security awareness requires ongoing reinforcement, realistic scenarios, and an organizational culture where security is a shared responsibility.
This is where most SMBs fall short. They don’t have the structure or resources to maintain awareness programs. The result is an organization of smart, well-intentioned people who are completely vulnerable to social engineering.
Building a Security Culture
Culture isn’t a technology. It’s a set of behaviors and values that become normal.
Organizations with strong security culture treat security as everyone’s job. Users report suspicious emails instead of ignoring them. Developers ask about security during code reviews. Executives budget for security improvements. Vendors are vetted before being granted access.
Creating this culture in an SMB is possible, though it requires sustained effort:
Leadership must champion it. Security is a topic leadership discusses and funds. If the owner doesn’t care, nobody else will.
Policies should be simple and clear. Overly complex security policies get ignored. If the rule is “don’t reuse passwords,” that’s clear. If it’s a 50-page security manual, nobody reads it.
Training should be regular and relevant. Quarterly training tied to actual threats you face beats a single annual webinar. Make it short, practical, and maybe even interesting.
Consequences should exist. If security policies have no teeth, they’re just suggestions. This doesn’t mean firing people for mistakes, but accountability matters.
Celebrate security wins. When someone reports a phishing email, thank them. When a system goes unbreached for a year, acknowledge it. Security isn’t punishment. It’s success.
How to Address the SMB Cybersecurity Challenge
The picture painted here is sobering, but hopeful. SMB targeting isn’t inevitable chaos. It’s a predictable pattern exploited by attackers operating at scale.
This is where solutions like phishing simulation platforms become essential for SMBs. Rather than treating employee training as a checkbox, organizations can run regular simulations that create a realistic sense of threat. Employees learn what phishing actually looks like. Organizations measure awareness over time. Training adapts based on results.
Dark web monitoring serves a different but critical function. Knowing that your credentials have been compromised before an attacker uses them changes everything. You can reset passwords, strengthen authentication, and monitor for abuse before actual damage occurs. For SMBs that lack threat intelligence infrastructure, this is the single fastest way to get ahead of known compromise.
Gamified training frameworks turn security from a chore into something users actually engage with. Points, leaderboards, and recognition make security participation voluntary rather than mandatory. Engagement increases. Retention improves. The organization gets more secure.
None of these solutions is a replacement for the fundamentals. Patching, backups, MFA, and network segmentation still matter. But they work alongside awareness and create a more complete picture of your actual security posture.
The Bottom Line
SMBs are now bigger targets because they represent a perfect balance of value and vulnerability. Attackers have engineered tactics specifically for environments with limited budgets and limited staff. The standard enterprise security playbook doesn’t apply.
But SMBs can compete. Start with the fundamentals: inventory, MFA, patching, backups, and segmentation. Layer on awareness training and dark web monitoring. Document your incident response plan. Build a culture where security is a shared responsibility.
These are not exotic tools or strategies. They’re basic discipline applied consistently. The companies that implement these measures survive breaches. The ones that don’t often don’t survive at all.
The good news is that you’re not starting from zero. The framework exists. You just need to execute it.
Check our latest the blog regarding How to Get Executive Buy-In for a Security Awareness Budget