

Shadow AI: What Happens When Employees Paste Company Data into Chatbots
A sales manager is racing toward a deadline. She pastes a customer contract into a public chatbot and asks for a summary. The answer comes back in seconds, and she moves on with her day. Nobody in IT ever hears about it.
This is shadow AI, and it is already happening in most organizations. Shadow AI means employees using AI tools that the company has not approved, reviewed, or secured. The tools are free, fast, and genuinely useful. That is exactly why the risk is so hard to contain.
This article explains what happens to data once it leaves the clipboard, why well-meaning staff create most of the exposure, and what security teams can do about it without banning everything.
What Shadow AI Actually Means
Shadow IT is an old problem. Employees have always used personal email, file-sharing apps, and unsanctioned software to get work done. Shadow AI is the latest version of the same habit.
The difference is what flows into these tools. A file-sharing app stores documents. A chatbot takes in text, processes it, and may keep it. People type or paste things into a chat window that they would never attach to an external email.
Most shadow AI use looks harmless on the surface. Someone wants a cleaner email, a faster summary, or help debugging a script. The intent is productive. The data handling is the problem.
Why Employees Do It
Employees do not paste data into chatbots to harm the company. They do it because the tools work and the pressure to deliver is constant.
Several things drive the behavior:
- Speed. A chatbot can draft, summarize, or translate in seconds.
- Easy access. Most tools need only a browser and a free account.
- No clear rules. Many companies have no AI policy, or one nobody remembers.
- Low perceived risk. A chat window feels private, like a conversation with a helper.
That last point matters most. People treat a chatbot like a calculator. It is not one. It is an external service run by a third party, with its own retention rules, its own staff access, and its own security posture.
What Happens to the Data After the Paste
The honest answer is that it depends on the tool, the account type, and the settings. That variation is itself part of the risk.
With some consumer-grade tools, the provider may retain conversations for a period of time. Some providers use conversations to improve their models unless the user opts out. Enterprise plans from the same vendors often come with different terms, including stricter retention and no training on customer data. The employee using a personal free account usually gets the weaker version.
Here is what security teams should keep in mind:
- Once data leaves your environment, you lose control over where it is stored and who can access it.
- A vendor’s retention policy can change, and you will likely not be notified.
- Vendor employees may be able to review conversations for safety or support purposes.
- Account compromise is a separate risk. If an attacker takes over an employee’s chatbot account, the full chat history may be exposed.
- Data pasted into a tool cannot be easily recalled. You cannot unsend it.
None of this means every chatbot leaks data. It means you cannot verify what happens to it, and your compliance obligations do not care about good intentions.
A Realistic Scenario: The Quarterly Report That Left the Building
Consider a mid-sized logistics company with about 800 employees. The finance team is preparing a board report. One analyst has a long spreadsheet export with unreleased quarterly figures, supplier pricing, and a list of customers who are late on payments.
She is behind schedule. She copies a large block of the data into a free chatbot and asks it to write an executive summary and flag anything unusual. The tool produces a decent draft. She edits it and sends it up the chain.
Three problems now exist, and nobody has noticed any of them.
First, unreleased financial figures sit in a third-party system. If the company is publicly traded or preparing a transaction, that may carry legal weight. Second, supplier pricing may be covered by confidentiality clauses in vendor contracts. Third, the customer payment data may include personal information subject to privacy law.
Nothing was hacked. No alert fired. No one broke in. An employee made a quick decision under time pressure, and the company’s data now lives somewhere it does not control.
Months later, during an audit or a customer questionnaire, someone asks a simple question: “Do you know where your sensitive data goes?” The honest answer is no.
The Types of Data Most Often at Risk
Not all pasted data carries the same risk. Still, certain categories show up again and again in real incidents and near-misses.
Source code and credentials. Developers paste code to debug it. That code sometimes contains API keys, database passwords, or internal architecture details. Secrets embedded in code are especially dangerous.
Customer and employee information. HR staff and support teams paste names, emails, case notes, and performance reviews to get help drafting responses. This is personal data, and privacy regulations apply.
Legal and contract text. Contracts, NDAs, and settlement language often go into chatbots for summaries. These documents frequently carry confidentiality terms of their own.
Financial and strategic material. Forecasts, pricing models, merger discussions, and board materials are high-value targets and high-consequence leaks.
Security information. Security staff sometimes paste logs, configurations, or vulnerability details to get faster analysis. That can hand an outside party a map of your environment.
Why Traditional Controls Miss It
Most security tooling was built to catch files leaving the network, malware arriving, or credentials being stolen. A person typing text into a web form looks like normal browsing.
Several gaps make shadow AI hard to see:
- Encrypted web traffic. Chatbot sessions run over standard HTTPS, so content is not visible without inspection tools.
- Personal devices. Employees may use a phone or home laptop, completely outside corporate monitoring.
- Browser extensions and plugins. Many AI add-ons read page content and send it elsewhere, often with broad permissions.
- Embedded AI features. AI assistants now appear inside everyday software. Staff may not even realize they are using one.
Data loss prevention tools can help, but they are not a complete answer. They work best when paired with clear policy and informed users. Technology alone will not close this gap, and it is worth being skeptical of any product that claims it will.
The Compliance and Legal Exposure
Shadow AI is not only a security issue. It is also a governance problem.
If your organization handles personal data, you likely have obligations around where that data goes and who processes it. Sending it to an unapproved vendor can breach those obligations, even if nothing bad ever happens afterward. The same applies to contractual duties with customers and partners.
Regulated industries face sharper consequences. Healthcare, finance, legal services, and public sector organizations often have strict rules about third-party processing. A single careless paste can create a reportable event.
There is also a plain trust issue. Customers who share data with your company expect you to protect it. They do not expect it to be pasted into a public tool to save an analyst twenty minutes.
Why Banning AI Tools Usually Fails
The instinct to block everything is understandable. It rarely works for long.
When a company bans AI outright, usage does not stop. It moves out of sight. Employees switch to personal phones, home networks, and personal accounts. You lose whatever visibility you had, and you lose the chance to guide behavior.
A ban also ignores a real business need. These tools do save time on legitimate tasks. If you offer no approved alternative, people will find their own.
The better approach is managed access. Give staff a sanctioned option, set clear rules about what data may be used, and make the safe path the easy path.
What Security Teams Can Do Right Now
You do not need a large budget to reduce shadow AI risk. Start with these steps.
- Find out what is already in use. Review web proxy logs, DNS data, and browser extension inventories. Survey staff, and make it clear the goal is understanding, not punishment.
- Write a short, plain AI use policy. Keep it to one page. State which tools are approved, which data types are off limits, and who to ask with questions.
- Classify your data in simple terms. Staff need to know what “confidential” means in practice. Use three or four categories and give real examples.
- Provide an approved tool. If budget allows, license an enterprise AI service with proper contractual protections. Check retention terms, training terms, and access controls before you buy.
- Apply technical guardrails. Use DLP rules, browser controls, and access policies to flag or block the most sensitive categories, such as source code, credentials, and customer records.
- Control browser extensions. Restrict installation to an approved list. Extensions with broad page access are a quiet exposure.
- Update vendor and third-party reviews. Ask suppliers whether they use AI tools on your data. Add the question to security questionnaires.
- Prepare an incident path. Decide in advance what happens when someone reports a paste. A no-blame process encourages people to speak up quickly.
- Train people, repeatedly. A policy nobody reads protects nothing. Awareness has to be ongoing, practical, and tied to real work situations.
Taken together, these steps will not eliminate the risk. They will shrink it and give you visibility you do not have today.
The Human Layer Is the Real Control Point
Every item on that list depends on one thing: what employees do in the moment, with a deadline looming and a chatbot one tab away.
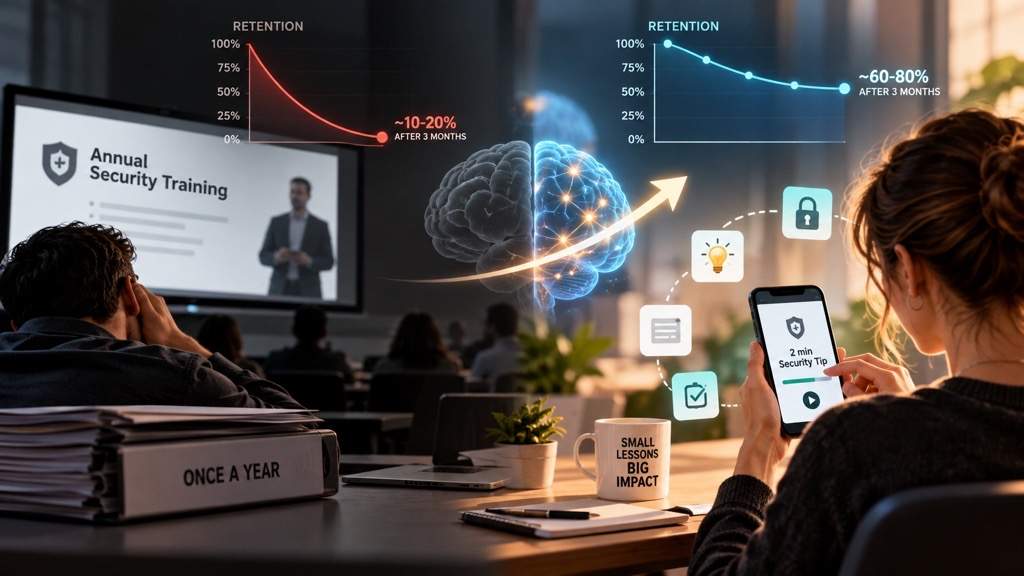
Policies are written once. Decisions are made hundreds of times a day. The gap between the two is a behavior problem, and behavior responds to training that feels relevant and memorable, not to annual slide decks.
Good awareness training does three things. It explains the “why” in plain language. It shows realistic situations, like the finance analyst above. And it gives people a fast, simple rule they can apply under pressure, such as “if you would not email it to a stranger, do not paste it into a chatbot.”
Security teams also need feedback. Who is struggling? Which departments take the most risks? Without data on human behavior, you are guessing.
How Cruxroot Fits Into This Problem
Shadow AI is one more reminder that people sit at the center of data security. Cruxroot is built around that idea, and its tools address the human side of this risk in practical ways.
Phishing simulations build the habit of pausing before acting. The same skill that helps an employee spot a suspicious link helps them stop before pasting a contract into an unknown tool. Simulations can also reveal which teams need more support.
Gamified training keeps awareness active instead of forgotten. Short, interactive modules based on realistic workplace scenarios, including AI use, help staff remember what to do when it counts. People retain what they practice.
Dark web monitoring covers the other end of the problem. If credentials or corporate data do surface in criminal marketplaces or breach dumps, early notice lets your team reset passwords and respond before an incident grows. It does not stop a paste from happening, but it helps you detect the downstream effects of exposure.
No single product solves shadow AI. Cruxroot works best as one layer alongside clear policy, sensible technical controls, and an approved set of tools. If you work with a managed service provider, ask them how awareness training and monitoring can fit into your broader security program.
Conclusion
Shadow AI is not a future threat. It is a present habit, driven by useful tools and busy people. Most of the employees involved mean well, and most do not realize they are creating risk.
The answer is not panic or blanket bans. Find out what is happening, set simple rules, offer safe alternatives, and keep training people on real situations. Visibility and good habits will do more than any single control.
Start with one question this week: do you know which AI tools your employees use today? If the answer is no, you have your first task
Check our latest the blog regarding “I Clicked the Link”: What Happens in the First 30 Minutes After a Phishing Click
