

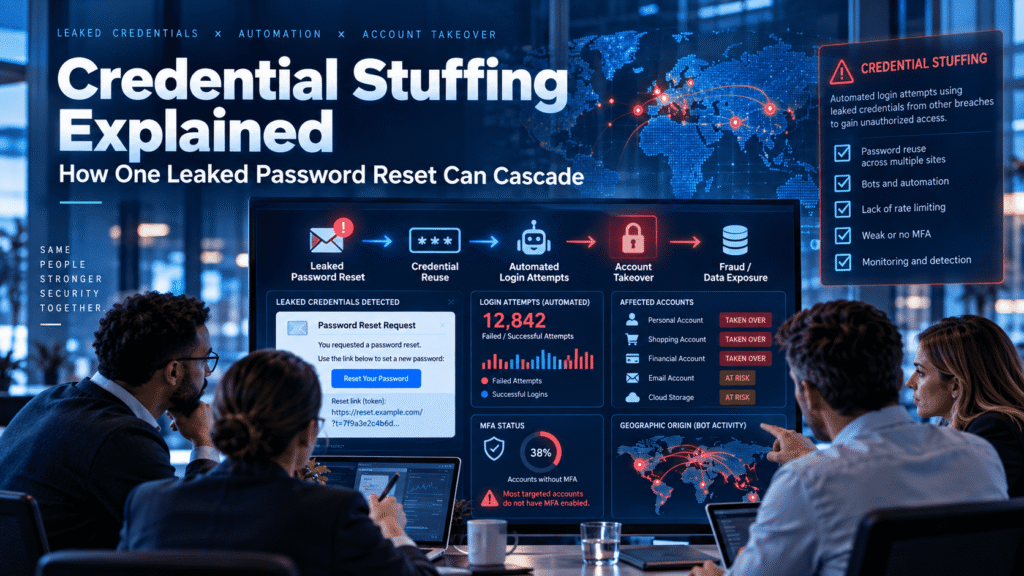
Credential Stuffing Explained: How One Leaked Password Reset Can Cascade
A developer at a SaaS company uses the same password across three systems: Gmail, the company VPN, and a contractor payroll platform. That password leaks in a data breach at a fitness app they signed up for months ago. They never received a breach notification. Three weeks later, attackers try that email and password combination on hundreds of services. One of them works.
That’s credential stuffing, and it’s not a theoretical threat.
Credential stuffing is the automated process of trying stolen username and password combinations across multiple online services, hoping a fraction will succeed. It’s simple, effective, and requires no advanced hacking skills. For security teams managing employee access across dozens of platforms, it represents a cascading vulnerability that compounds with every password reuse in the organization.
This isn’t just about individual accounts getting compromised. When an employee’s credentials are stuffed into your VPN, email, or cloud infrastructure, the entire company is exposed. One leaked password becomes a foothold for lateral movement, data exfiltration, and persistence inside your network.
Understanding how credential stuffing actually works, and where the cascade accelerates, is the first step toward stopping it.
What Credential Stuffing Actually Is
Credential stuffing relies on a simple assumption: people reuse passwords. It’s not brute force. Attackers aren’t guessing random combinations. They’re using real credentials harvested from previous breaches, sold on underground forums, or leaked in bulk. If your email and password were exposed in any recent data breach, chances are attackers already have them.
The attack works like this: attackers obtain a database of stolen credentials, usually containing millions of email and password pairs. They write a script or use an automated tool to submit these credentials against a target service’s login page. The script loops through hundreds of thousands of combinations in minutes. Any successful match gets flagged for follow-up exploitation.
The barrier to entry is incredibly low. Attackers don’t need custom tools. Pre-built credential stuffing platforms exist on the dark web, some offered as-a-service for a few hundred dollars per month. The script runs unattended. The attacker waits for hits and then monetizes them.
What makes credential stuffing different from other password attacks is its scale and passivity. The attacker isn’t trying to crack your specific password. They’re leveraging the fact that your password was compromised elsewhere, long before they target you.
Why Passwords Cascade Across Services
The cascade begins with a simple human behavior: password reuse. Security awareness training covers this constantly, yet employees continue to reuse passwords because remembering dozens of unique, complex strings is genuinely difficult.
Worse, employees often use password patterns. A base password with variations becomes the norm. “CompanyName2024” becomes “CompanyName2024!” on the VPN and “companyname2024” on an older system. An attacker who cracks one gains hints about the others.
When one service is breached, all accounts using that password become immediately vulnerable. A compromise at a consumer service like Spotify, LinkedIn, or a fitness app gives attackers valid credentials for the employee’s work email. From work email, they can reset passwords on connected services: cloud storage, project management tools, VPN access, financial systems.
The cascade accelerates because most organizations use single sign-on (SSO) or linked accounts. Compromise email, and you’ve potentially compromised dozens of downstream services that trust it for authentication.
Consider a scenario: an employee reuses their work email password on an old GitHub account. The GitHub account remains dormant for years. A breach exposes the password. An attacker tries it against the work email. It works. The attacker uses account recovery on the email to set a new password. They’re now in. From the email account, they reset the password on Slack, Google Workspace, Jira, the VPN, and the cloud infrastructure. Within 30 minutes, the attacker has lateral access across the entire company’s stack.
This is credential stuffing’s real danger: it’s not about stealing one password. It’s about infiltrating the entire authentication chain.
How the Cascade Becomes a Security Incident
The cascade moves through predictable stages, and recognizing them is critical for incident response.
Stage One: Initial Compromise. The employee’s credentials are exposed in a breach they never learn about. Months pass. Attackers obtain the dump and begin credential stuffing attacks.
Stage Two: First Success. The attacker finds a working credential, usually on a non-critical service first. Email, SaaS app, or social media. They test access. If it works, they move to the next target.
Stage Three: Lateral Movement. Once inside a primary account like email or a cloud provider, the attacker leverages it to reset passwords elsewhere. They enable forwarding on email, add themselves as a recovery contact on linked accounts, or use the email to authenticate to SSO systems.
Stage Four: Persistence. The attacker creates backdoors. They add a secondary account, enable API access, or establish a foothold that persists even if the original password is changed. They disable MFA if it’s not enforced. They extract data or set up long-term access for future exploitation.
Stage Five: Discovery (if lucky). Your security team notices unusual login activity, a suspicious IP, changed account settings, or suspicious email forwarding rules. Depending on your logging and monitoring, this might happen hours, days, or weeks after initial compromise.
The cascade is dangerous because each stage multiplies the damage. One leaked password becomes multiple compromised accounts, which becomes unauthorized network access, which becomes data exfiltration or ransomware deployment.
Organizations often detect stage four or five, not stage one. By then, attackers have been inside for weeks.
A Realistic Scenario: How One Password Becomes a Breach
Here’s how credential stuffing played out in a real incident:
A mid-market consulting firm with 150 employees uses Google Workspace, Slack, Asana, Jira, and a custom intranet. The team lead on a major client project uses the same password everywhere: his first name, birth year, and an exclamation mark. It’s complex enough to pass requirements but weak against dictionary attacks.
That password was exposed six months ago when a B2B vendor he signed up for suffered a breach. The vendor never disclosed it publicly. The employee was never notified. The credentials ended up on a paste site used by credential stuffing operations.
An attacker running automated stuffing attacks against Slack business emails targets the consulting firm’s Slack workspace. The team lead’s email and password work. The attacker logs in.
Slack is configured with SSO through Google Workspace, but the Slack API is exposed. The attacker downloads the member list and channel names. They browse public and private channels, finding client names, project details, and internal conversations about rate negotiations with a major prospect.
The attacker then attempts the same email and password on Google Workspace. It works. Now they have access to email, Google Drive, and Google Meet recordings. They enable email forwarding to an external address, then change the password. They create API credentials to maintain access. They create a Google Drive folder in the user’s drive with a naming convention that blends in (like “2024_Archive_Draft”). Over the next week, they download sensitive client documents.
The team lead notices his password was changed when he tries to log in the next morning. He calls IT. IT resets his password and assumes it was a simple mistake or a phishing attack the user doesn’t remember. They don’t investigate further.
Three weeks later, a client calls asking why their rate proposal document was being discussed on an external email address. The consulting firm launches an investigation and discovers the breach. Forensics reveals the initial access was via credential stuffing, and the attacker maintained access for 21 days undetected.
The damage: client confidentiality breached, legal liability, brand damage, and the cost of forensics and remediation. All because one password was reused.
Why Credential Stuffing is Accelerating
Credential stuffing attacks are increasing because the fundamental conditions are worsening.
First, breaches are exploding in volume and size. Every month, new databases of millions of credentials appear on dark web forums and paste sites. Attackers have larger and more diverse credential sets to work with. The probability of a match improves simply because there’s more data in circulation.
Second, the tools have become frictionless. Automated stuffing platforms handle rate limiting, IP rotation, and bot detection bypass. An attacker with zero technical skills can launch a campaign in an afternoon.
Third, human behavior hasn’t changed. Employees still reuse passwords at scale. Surveys and behavioral studies consistently show that password reuse is the norm, not the exception, across all skill levels. IT departments enforce strong password policies on corporate accounts, but employees still use simple, reused variations across services they control personally (consumer apps, old systems, contractor platforms).
Fourth, not all password breaches are disclosed or tracked. A small SaaS tool a contractor uses, an older platform that never made headlines, a lesser-known social network—these breaches often don’t trigger employee notifications. Attackers find these credentials and use them as entry points weeks or months later.
This is why credential stuffing is often called the “silent” attack. By the time it’s detected, it’s usually too late.
What Security Teams Can Actually Do
Stopping credential stuffing requires layers, not a single fix. Password managers and MFA are foundational, but organizational practices and visibility matter too.
Enforce Multi-Factor Authentication (MFA) everywhere. This is the closest thing to a credential stuffing vaccine. If an attacker has your email and password but not your authenticator, they’re stopped. MFA doesn’t prevent the credential stuffing attempt, but it prevents the compromise. The caveat: MFA must be enforced across all systems, including cloud infrastructure, VPNs, and third-party services. Partial enforcement leaves gaps.
Monitor for and respond to breaches affecting employee email addresses. Use a dark web monitoring service to track if employee email addresses appear in new breaches. When a breach is detected, require immediate password changes on all corporate systems. This is reactive, but it closes the window before attackers weaponize the exposed credentials. Response time matters. If you detect a breach and reset the password within 24 hours, the risk drops significantly.
Disable password reuse in identity management systems. Most organizations allow users to create passwords with minimal restrictions. Enforce rules that prevent password reuse across systems. This doesn’t prevent employees from reusing the same password outside your systems, but it reduces the blast radius if one service is compromised.
Audit and remove unused integrations. Credential stuffing often succeeds against forgotten or dormant accounts. An old GitHub account, an inactive SaaS tool, or a contractor platform linked to the employee’s work email becomes an entry point. Periodically audit third-party service access and remove unnecessary integrations.
Implement conditional access policies. Modern identity platforms allow you to restrict authentication based on risk signals. Block logins from unusual geographies, unusual times, or devices that haven’t accessed the system before. If an attacker compromises credentials and tries to log in from a foreign IP at 3 AM, the conditional access policy flags or blocks it. This prevents attackers from immediately accessing your systems even if they have valid credentials.
Deploy deception and monitoring. Place honeypot accounts (fake employee credentials) in your systems. If these accounts are accessed, it’s 100% an attack. Alert on any authentication attempt from an obviously compromised credential source.
Segment network access. Even if an attacker gains credentials, limit what those credentials can access. A contractor’s credential should not grant access to the finance system. A junior employee’s credential should not grant access to the CEO’s email. Segmentation limits the blast radius if any single credential is compromised.
Run regular phishing and credential simulations. This isn’t directly preventing credential stuffing, but it reinforces awareness. Employees who understand the cascade of a compromised password are more likely to use unique passwords and enable MFA in their personal accounts. Simulations can also test whether employees fall for credential harvesting attacks that set the stage for stuffing.
The common thread across these steps is visibility and response speed. You can’t prevent every credential from being exposed somewhere, but you can detect when it’s exposed, enforce MFA to prevent compromise, and respond before attackers weaponize the credentials.
Where CruxRoot Fits Into Your Defense
The practical steps above require employee awareness and compliance. Phishing simulations and dark web monitoring are two ways CruxRoot helps security teams execute this strategy.
Dark web monitoring alerts you when employee credentials appear in leaked databases. Instead of waiting for an employee to notice unauthorized access, you’re notified immediately. You can reset passwords, enforce MFA reviews, and segment access before attackers attempt a stuffing campaign.
Phishing simulations reinforce the connection between weak passwords, reused credentials, and organizational risk. Employees who’ve seen simulations of how a credential compromise leads to lateral movement and data theft are more likely to enable MFA and avoid reusing passwords. Gamified training makes the lessons stick.
These tools work alongside technical controls (MFA, conditional access, monitoring) to close the gap between what security policy says and what employees actually do.
The Real Cost of Credential Stuffing
Organizations often underestimate credential stuffing because it doesn’t always leave obvious traces. An attacker can sit inside your network for weeks, extracting data or preparing ransomware deployment, without triggering alerts.
The costs compound: detection and response, credential reset operations, forensics, legal and compliance notifications, potential breaches of customer data, reputation damage, and the operational friction of enforcing MFA and password management across hundreds of employees.
All of this stems from one leaked password that the employee never even knew was exposed.
The good news is that credential stuffing is preventable. It doesn’t require zero-day exploits or social engineering. It’s just automation running against bad luck (password reuse, no MFA, no monitoring). Close these gaps, and you’ve eliminated one of the most common attack vectors in the threat landscape.
Check our latest the blog regarding NIS2 What it Means for Security Awareness Programs
